Dapr Sentry control plane service overview

Overview of the Dapr sentry service

The Dapr Sentry service manages mTLS between services and acts as a certificate authority. It generates mTLS certificates and distributes them to any running sidecars. This allows sidecars to communicate with encrypted, mTLS traffic. For more information read the sidecar-to-sidecar communication overview.

On Kubernetes, Sentry also stamps the requesting pod’s container image references into each issued workload certificate as a custom X.509 extension, giving downstream systems verifiable supply-chain provenance of the software behind each workload identity.

Self-hosted mode

The Sentry service Docker container is not started automatically as part of dapr init. However it can be executed manually by following the instructions for setting up mutual TLS.

It can also be run manually as a process if you are running in slim-init mode.

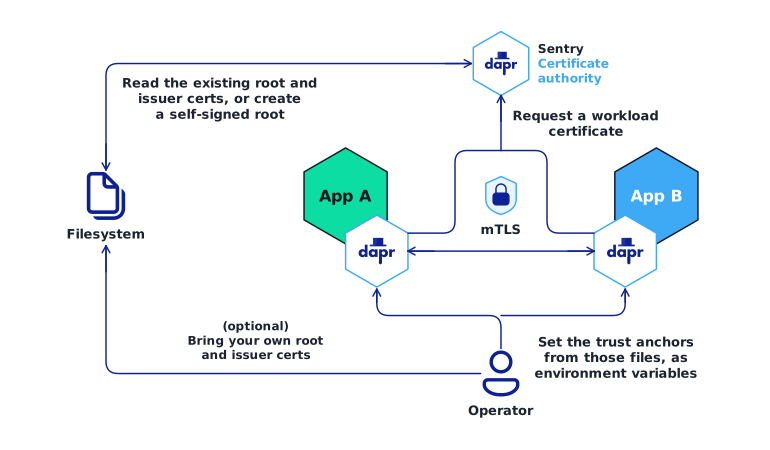
Sentry issuing workload certificates in self-hosted modeA filesystem mark on the left holds the certs. A line with a head at each end leaves its top, runs up and along to Sentry, the Dapr certificate authority, which stands above the middle of the picture, and is labelled "Read the existing root and issuer certs, or create a self-signed root". To the right of the filesystem and on the same line, App A and App B each run beside a Dapr sidecar, and the two sidecars are joined by a line with a head at each end carrying a shield and padlock marked mTLS. A line leaves each sidecar on the side facing the other and rises between the two apps, where the pair merge into one arrow into the bottom of the Sentry hexagon, labelled "Request a workload certificate". Below the apps an operator figure stands in the middle. One run goes up from the operator and forks into both sidecars, labelled "Set the trust anchors from those files, as environment variables"; another leaves the operator sideways and reaches the filesystem, marked optional, because the operator may bring existing root and issuer certs.FilesystemRead the existing root andissuer certs, or createa self-signed rootSentryCertificateauthorityApp AApp BmTLSRequest a workloadcertificateOperatorSet the trust anchorsfrom those files, asenvironment variables(optional)Bring your own rootand issuer certs

Kubernetes mode

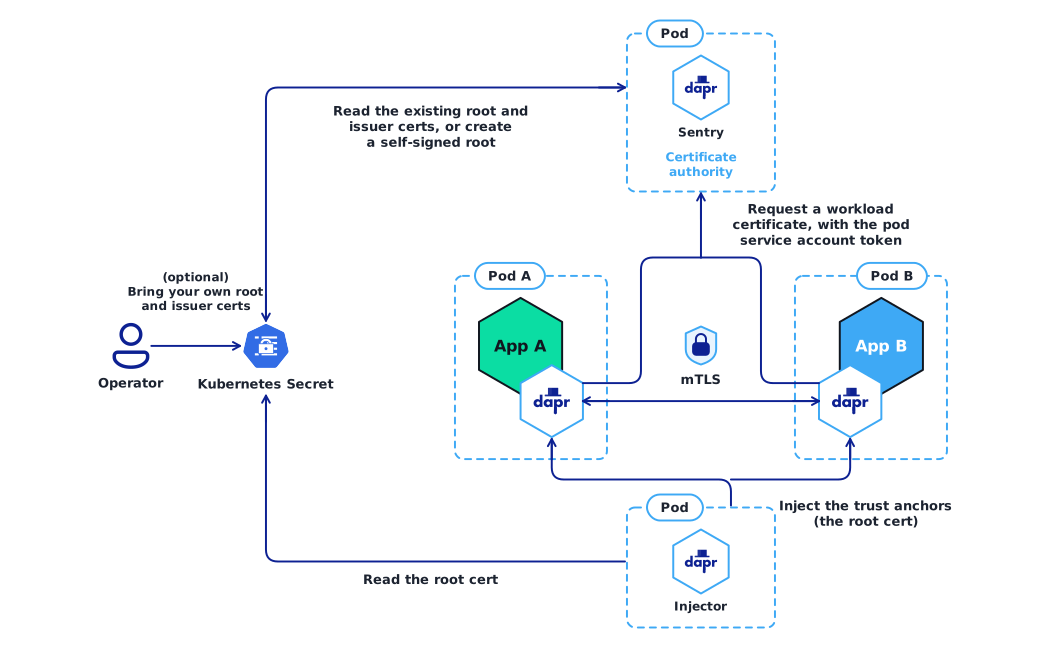
The sentry service is deployed as part of dapr init -k, or via the Dapr Helm charts. For more information on running Dapr on Kubernetes, visit the Kubernetes hosting page.

Sentry issuing workload certificates on KubernetesOn the left of the middle row, an operator figure stands beside a Kubernetes Secret holding the certs, with an arrow from the operator into the secret marked optional, because the operator may bring existing root and issuer certs. A line with a head at each end leaves the secret's top, runs up and along to Sentry, the Dapr certificate authority, which stands in a pod of its own above the middle of the picture, and is labelled "Read the existing root and issuer certs, or create a self-signed root". To the right of the secret and on the same line, App A and App B each run beside a Dapr sidecar in a pod of their own, and the two sidecars are joined by a line with a head at each end carrying a shield and padlock marked mTLS. A line leaves each sidecar on the side facing the other and rises between the two app pods, where the pair merge into one arrow into the bottom of Sentry's pod, labelled "Request a workload certificate, with the pod service account token". A row below the apps, the injector stands in a pod of its own between them. One run leaves its top and forks into both sidecars, labelled "Inject the trust anchors (the root cert)"; another leaves its side, passes under the apps and reaches the secret, labelled "Read the root cert".OperatorKubernetes Secret(optional)Bring your own rootand issuer certsRead the existing root andissuer certs, or createa self-signed rootPodSentryCertificateauthorityPod APod BApp AApp BmTLSRequest a workloadcertificate, with the podservice account tokenPodInjectorInject the trust anchors(the root cert)Read the root cert

Additional sentry container arguments

Use the dapr_sentry.extraArgs Helm value to pass extra command-line arguments to the sentry container. Use this value for sentry flags that have no dedicated Helm value. The value is a list of strings. It defaults to []. Dapr appends each argument after the built-in sentry container arguments.

dapr_sentry:
  extraArgs:
    - "--jwt-ttl=48h"
    - "--healthz-listen-address=127.0.0.1"

--healthz-listen-address sets the address the sentry healthz server listens on, and --metrics-listen-address sets the address of its metrics server. Both default to all interfaces.
Further reading